

排序
利用动态链接共享对象库进行Linux提权

Learn how to exploit weak file permissions and hardcoded RPATH in dynamically linked shared object libraries for Linux privilege escalation. Explore prevention
 9年前
利用userinit注册表键实现无文件后门
了解如何利用Userinit注册表键在Windows系统中实现无文件后门,提高隐蔽性和绕过杀毒软件的能力。本文详细介绍技术细节和测试方法。
9年前InsecurePowerShell:不用类库System.Management.Automation
了解如何使用InsecurePowerShell执行PowerShell脚本,无需依赖System.Management.Automation.dll。本文探讨了不安全的功能移除及其实现原理。
9年前GoAhead Web Server远程代码执行漏洞分析(附PoC)
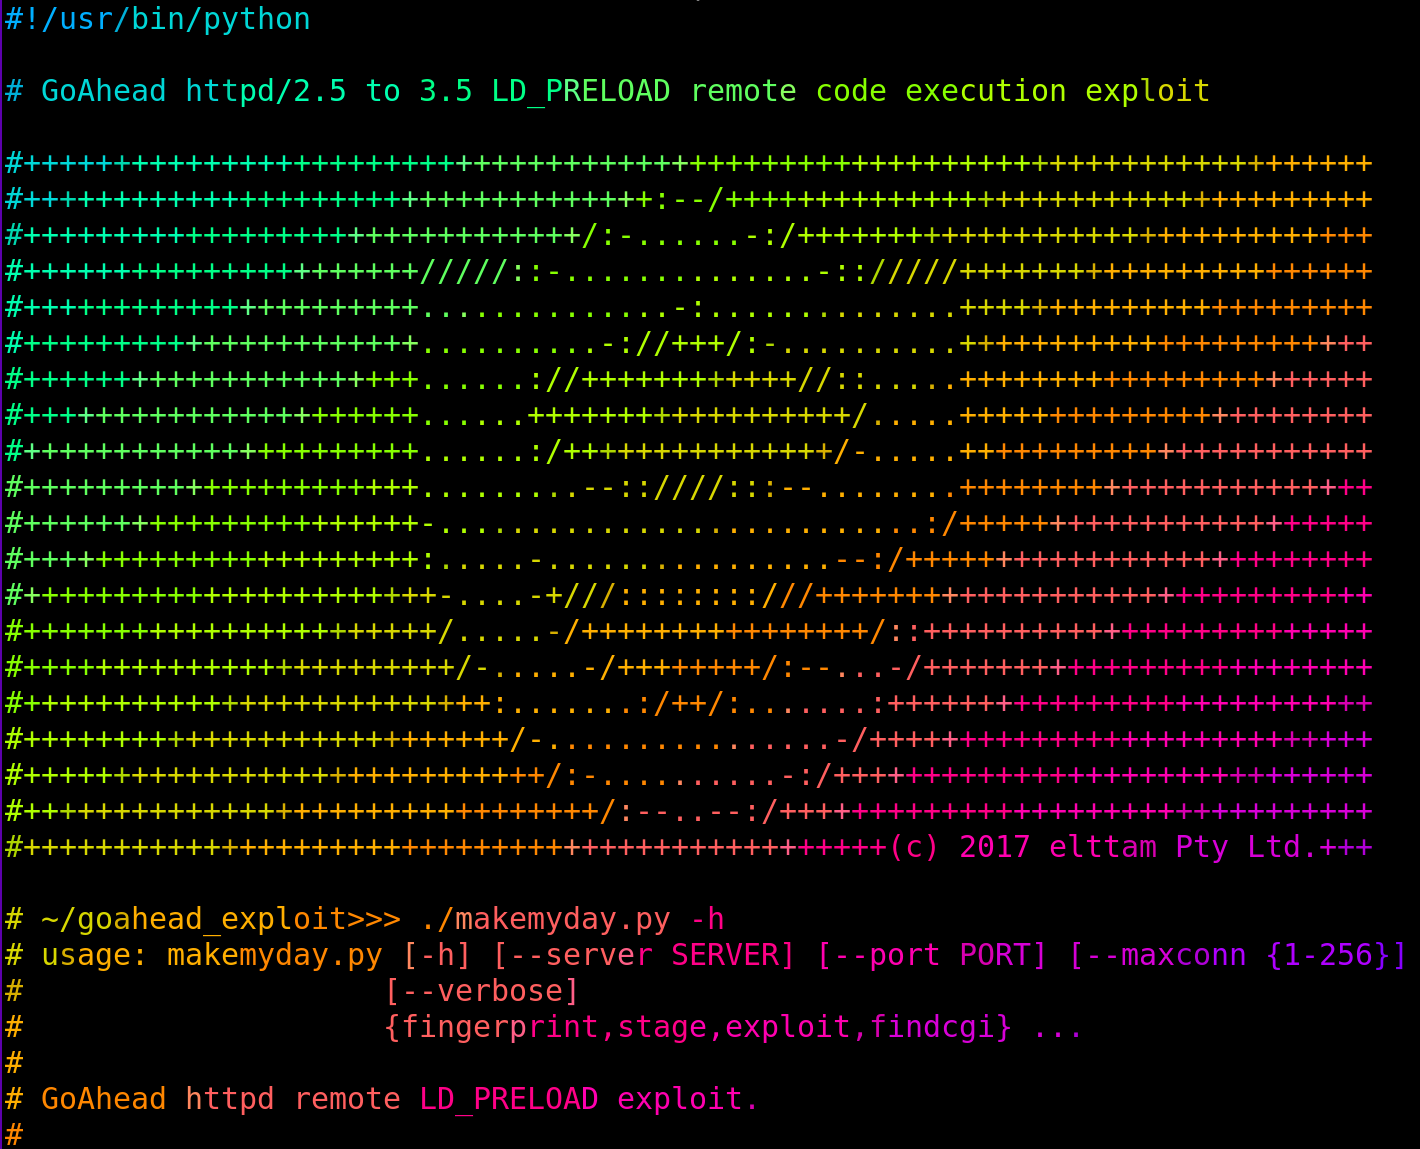
This article analyzes the GoAhead web server remote code execution vulnerability (CVE-2017-17562) and provides a PoC. The vulnerability occurs due to untrusted
9年前Captcha插件后门分析和修复

文章详细解析了Captcha插件在4.3.6至4.4.4版本中的后门问题,包括触发条件、影响范围及应对措施。
9年前如何基于Python写一个TCP反向连接后门
Learn how to develop a reverse TCP connection backdoor using Python. This tutorial provides step-by-step instructions for creating secure and undetectable remot
9年前如何利用Docker构建命令控制服务器

Learn how to leverage Docker for building efficient and secure command control servers in cybersecurity operations. Discover the benefits of using Docker for au
9年前看不见的攻击面:查看SQLite数据库就中招?

了解Navicat客户端在查看SQLite数据库字段时的XSS漏洞,如何被利用以读取敏感文件。
9年前Cobalt Strike实战技巧持久性权限控制姿势

本文详细介绍如何使用Cobalt Strike进行持久化权限控制,包括创建监听器、Scripted web_Delivery以及设置powershell开机自启动服务等实战技巧。
9年前我是如何利用CSRF Get DedeCms Shell的
本文详细介绍了如何通过CSRF攻击在DedeCms系统中植入WebShell的方法,包括具体代码分析与利用技巧。
9年前SMB共享之SCF文件攻击解析

了解如何利用SCF文件进行SMB共享攻击,获取NTLM/LANMAN哈希和Meterpreter Shell。安全客专业解析SMB协议中的漏洞与防护策略。
9年前GoAhead远程代码执行漏洞(CVE-2017-17562)分析及实战

This article analyzes the GoAhead Remote Code Execution Vulnerability (CVE-2017-17562) and demonstrates practical exploitation on a B-LINK router. Key points in
9年前